A healthcare app can have working patient dashboards, doctor accounts, and health tracking features and still lack important protections for patient information.
If you’re building with Lovable, you may be able to create these features quickly. But how do you control who can access medical records, keep track of changes, or prevent sensitive information from being exposed when someone leaves a device unattended?
These aren’t concerns that only appear after your application launches. They’re part of building a healthcare product that can support patients, providers, and the people responsible for managing it.
The good news is that adding stronger security controls doesn’t necessarily mean rebuilding your application.
In this guide, we’ll walk through seven HIPAA-related safeguards for healthcare applications and show how we implemented them using Lovable. We’ll use VitalWatch, a remote patient monitoring application, to demonstrate the features and how they work in practice.
Explore the Lovable Healthcare App Development Series
- Part 1: AI App Development with Lovable: From Idea to Working MVP — Build the healthcare application’s core features.
- Part 2: From AI Prototype to Production: How to Build Scalable AI Applications — Strengthen the application’s architecture and production readiness.
- Part 3: How to Make a Lovable App HIPAA Compliant — Implement HIPAA-related security safeguards.
- Part 4: How to Build a Production-Ready HIPAA-Compliant App with Lovable — Bring the development process together in a reusable guide.
Can You Make a Lovable App HIPAA Compliant?
Lovable can help you implement technical safeguards that support HIPAA requirements, including access restrictions, audit logging, automatic session management, and controls for protecting patient information.
The HIPAA Security Rule establishes standards for protecting electronic protected health information (ePHI). These include technical safeguards as well as administrative and physical requirements.
For healthcare founders, the practical challenge is understanding which protections their application needs and how to incorporate them into existing workflows.
We used VitalWatch to implement and review these safeguards without rebuilding the application from scratch.
Step 1: Implement Role-Based Access Controls
HIPAA’s access control requirements focus on ensuring that electronic protected health information is available only to people or systems with appropriate authorization.
For healthcare founders, this means defining what each type of user can access rather than relying on separate dashboards to protect information.
A doctor may need access to assigned patients, while an administrator may need to approve doctors and manage accounts without reviewing patients’ clinical details.
How We Implemented Access Controls in VitalWatch
VitalWatch has three main roles: patients, doctors, and administrators.
We used Lovable to strengthen the permissions associated with each role:
- Patients can view and manage their own readings.
- Doctors can review information belonging to assigned patients.
- Administrators can manage accounts, approve doctors, and assign patients without unrestricted access to clinical information.
The administrator dashboard includes user management, doctor approvals, patient assignments, and account controls.
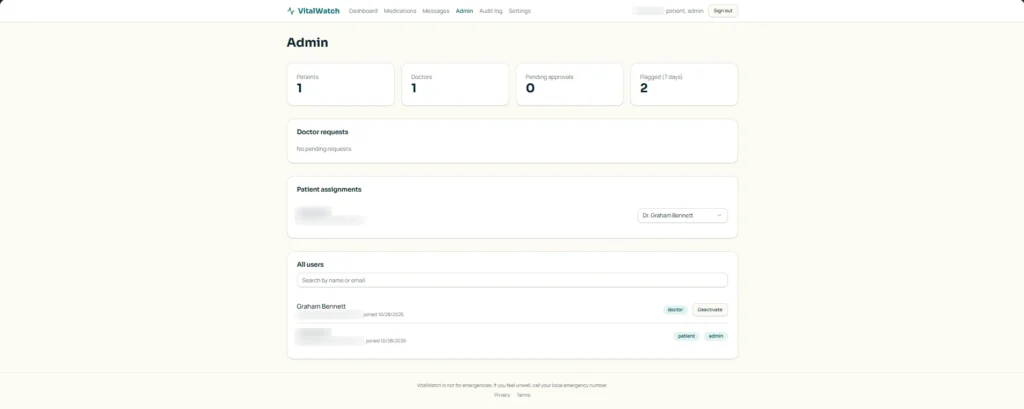
This separation is important because managing a healthcare application should not automatically give someone permission to view all the medical information it contains.
Step 2: Protect Patient Records and Preserve Important Changes
HIPAA includes requirements for protecting electronic health information against improper alteration or destruction.
For a healthcare application, that means thinking beyond whether users can create and view records. Founders also need to consider what happens when information is changed or removed.
For example, if a patient removes a blood pressure reading, the application may need to preserve information about the original record and the removal.
How We Protected Records in VitalWatch
We used Lovable to implement soft deletion for readings and medications.
When patients remove these records, they disappear from active views but remain stored in the database. The application also captures information about who removed the record and when.
During testing, we confirmed that two removed health readings remained stored with their removal details.
This allows the application to preserve record history while keeping removed information out of normal patient and doctor workflows.
We also reviewed six database audit fields that support record tracking:
| Field | Purpose |
|---|---|
| created_at | When a record was created |
| created_by | Who created it |
| updated_at | When a record was modified |
| updated_by | Who modified it |
| deleted_at | When a record was removed from active use |
| deleted_by | Who removed it |
VitalWatch captures relevant information through existing fields, including archived_at and archived_by for removed records. The exact tracking structure varies between tables rather than using all six field names everywhere.
For founders, the key consideration is whether the application can preserve important record history and establish what happened when information changes.
Step 3: Implement HIPAA Audit Logging
Audit controls help organizations record and examine activity in systems that contain or use electronic protected health information.
This becomes particularly important when a patient questions a missing record, an employee’s access needs investigation, or unusual account activity occurs.
An Audit Log should help authorized personnel understand what happened without unnecessarily exposing patient medical information.
How We Implemented Audit Logging in VitalWatch
We used Lovable to add a centralized Audit Log that records important events, including sign-ins, patient record access, administrative activity, and record removals.
The underlying events are stored in the database, while an administrator-facing page allows authorized users to review relevant activity inside VitalWatch.
The Audit Log displays six columns:
| Column | Information |
|---|---|
| When | When the event occurred |
| Who | The recorded user or system actor |
| Action | What activity took place |
| Patient | The related patient or record reference |
| Result | The outcome of the activity |
| Details | Additional information about the event |
These entries provide information about system activity without displaying the actual clinical values contained in patient readings.
Administrators should only have access to the audit information needed for their authorized responsibilities.
We also tested audit logging alongside record removal. When two test readings were removed, the records remained stored in the database and corresponding removal events appeared in the Audit Log.
This gives healthcare organizations a way to investigate significant activity while separating security oversight from access to clinical information.
Step 4: Add Automatic Session Timeouts
HIPAA’s technical safeguards include automatic logoff as an addressable implementation specification under access control.
Automatic logoff helps reduce the risk of unauthorized access when a user leaves an application open.
Consider a doctor reviewing patient information who steps away from a shared workstation. Without an inactivity timeout, the session could remain accessible to someone else.
How We Implemented Session Management in VitalWatch
We used Lovable to add automatic session management.
After 14 minutes of inactivity, VitalWatch displays a warning. If the user does not respond, the application signs them out after 15 minutes.
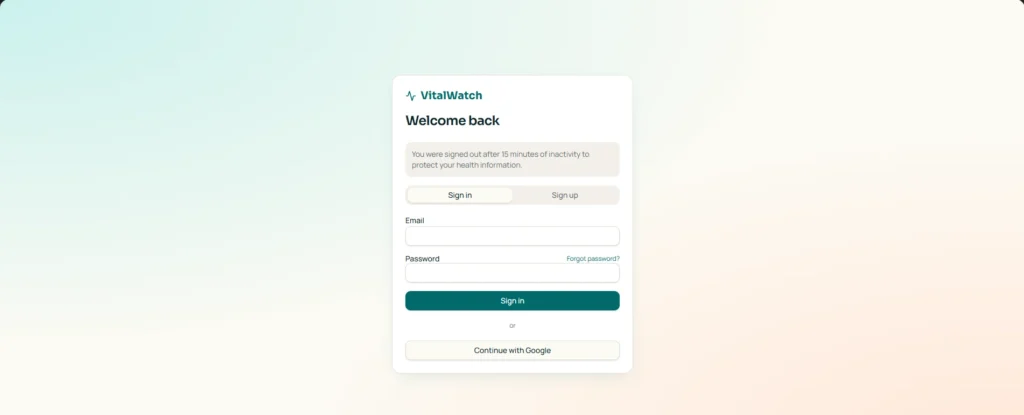
Users can choose to remain signed in when the warning appears.
The implementation also includes coordination between browser tabs and a Sign out of all devices option.
During preview testing, the warning appeared, the option to remain signed in worked, and returning to the dashboard after sign-out was blocked.
The 15-minute duration was selected for VitalWatch; HIPAA does not prescribe a universal session timeout for every application.
For healthcare founders, session management is especially important when applications are used across clinics, offices, and other environments where staff may be interrupted during their work.
Step 5: Monitor Security Activity
HIPAA’s security management requirements include reviewing information system activity, such as audit logs and security incident tracking.
For healthcare organizations, this means having visibility into activity that could indicate a problem.
Repeated failed sign-ins, blocked access attempts, unexpected role changes, or unusually high patient record access may warrant investigation.
How We Added Security Monitoring in VitalWatch
We used Lovable to add a security monitoring summary to the administrator-facing Audit Log page.
It displays five indicators:
- Failed sign-ins during the previous 24 hours.
- Blocked access attempts during the previous 24 hours.
- Role changes during the previous seven days.
- Night-time record views during the previous seven days.
- Users with unusually high record-viewing activity during the previous 24 hours.
These indicators help administrators identify activity worth investigating without displaying patients’ medical readings.
They provide monitoring visibility rather than a verified automated threat-detection system.
As a healthcare application grows, this type of oversight becomes increasingly useful for managing more accounts, staff, and patient interactions.
Step 6: Manage User Access and Account Changes
Access management is not a one-time task. Healthcare organizations need processes for granting, changing, and removing access as responsibilities change.
A doctor may leave a practice. An administrator may change roles. A staff member may no longer need access to the application.
Without appropriate account controls, former users could retain access they no longer require.
How We Strengthened Account Management in VitalWatch
We used Lovable to strengthen administrative account controls.
Administrators can deactivate user accounts while preserving associated records.
Additional protections help prevent accidental removal of the final administrator and inappropriate changes to administrative privileges.
The application also supports patient assignments and doctor approvals through its administrative interface.
These features help healthcare organizations manage access as teams change without giving administrators unrestricted access to clinical records.
For founders, the important consideration is whether the application’s permissions can be maintained as the business grows—not simply whether the first few user accounts work correctly.
Step 7: Document the Technical Safeguards
HIPAA requires covered entities and business associates to maintain applicable policies, procedures, and required documentation relating to security safeguards.
For founders, documenting application security features is also useful when working with developers, healthcare partners, or security reviewers.
A clear record of implemented safeguards makes it easier to understand how the application protects information and what further work may be needed.
How We Documented VitalWatch’s Safeguards
After implementing the security features, we used Lovable to generate a technical safeguards report.
The report describes the application’s access controls, audit logging, record protection, session management, security monitoring, and administrative controls.
It also identifies additional technical and organizational considerations relevant to healthcare launch preparation.
This documentation provides a useful reference for future security reviews and development decisions. It complements, rather than replaces, an organization’s required HIPAA documentation.
Building a healthcare application with Lovable or another AI development tool? Our HIPAA checklist helps you review important security and compliance considerations, including patient data protection, access management, and launch preparation.
What Else Is Needed Before Using Real Patient Data?
Technical safeguards are an important part of preparing a healthcare application for HIPAA requirements.
Before handling real patient information, organizations must also address applicable infrastructure, contractual, and operational responsibilities.
These include appropriate Business Associate Agreements (BAAs), security risk analysis, testing, access-management policies, incident response, backup and recovery, and record-retention practices.
The HHS guidance on HIPAA and cloud computing explains how cloud service providers and healthcare organizations must address their responsibilities when electronic protected health information is involved.
For VitalWatch, additional security work includes multi-factor authentication for privileged users, stronger session-token revocation, and verification of infrastructure and long-term audit-log retention.
These considerations should be addressed as part of preparing the application for real patient use.
How Technology Rivers Helps Healthcare Founders Build Secure, Scalable Applications
AI development tools like Lovable can help founders create healthcare applications and add important security features faster.
But as more patients, providers, and staff begin using an application, those features must work together within a secure and maintainable system.
Access controls need to remain effective as user roles change. Patient information must stay protected across workflows. Audit logging and monitoring should support security oversight without exposing unnecessary clinical details.
Technology Rivers helps healthcare founders and organizations address these requirements through healthcare software development, including application architecture, security implementation, integrations, and ongoing product development.
Our experience with remote patient monitoring solutions reflects the importance of designing applications around both clinical workflows and operational needs.
Frequently Asked Questions
Can you make a Lovable app HIPAA compliant?
Lovable can help implement technical safeguards that support HIPAA requirements, including access controls, audit logging, session management, and patient data protection.
Compliance also depends on applicable infrastructure, contractual, administrative, and physical safeguards.
Does Lovable sign a Business Associate Agreement (BAA)?
Whether a BAA is available depends on Lovable’s current service terms, the specific services being used, and the applicable agreement.
Healthcare founders should verify the provider’s current BAA availability and scope before using the service to handle electronic protected health information.
Can I add HIPAA safeguards to an existing Lovable app without rebuilding it?
In some cases, yes. If the existing architecture supports appropriate access controls, audit logging, record protection, and other safeguards, these features may be added without rebuilding the entire application.
The decision depends on the current system design and security requirements.
Can a Lovable healthcare app store real patient data?
A healthcare application may handle real patient information only when its deployment and operation meet applicable HIPAA requirements, including appropriate safeguards and vendor agreements.
The fact that an application was built using Lovable does not establish whether its particular hosting and service arrangements are suitable for electronic protected health information.
Do I need a developer to implement HIPAA safeguards in Lovable?
Lovable can help generate and implement security features, but professional development and security expertise may be needed to verify access restrictions, assess infrastructure, test controls, and address healthcare-specific requirements.
The level of assistance depends on the application’s complexity and the information it handles.
How much does it cost to make a Lovable app HIPAA-ready?
Costs depend on the application’s existing architecture, hosting environment, integrations, security controls, and the additional work required.
A technical assessment can help identify necessary changes before estimating the investment.
Final Verdict: Adding HIPAA-Related Safeguards to a Lovable App
Building a healthcare application with Lovable can extend beyond creating functional patient dashboards and provider workflows.
In VitalWatch, we implemented role-based access controls, protected record removal, centralized audit logging, automatic session management, security monitoring, and administrative protections.
These features demonstrate how AI development tools can help healthcare founders incorporate technical safeguards that support HIPAA requirements while continuing to build their products.
The important consideration is how these safeguards work together to protect patient information, support authorized access, preserve record history, and provide appropriate security oversight.
In Part 4 of our Lovable series, we’ll bring the development process together into a reusable guide for building a healthcare application with Lovable.